Recently i have a regular Keycloak deployment with the high level concept like below image,
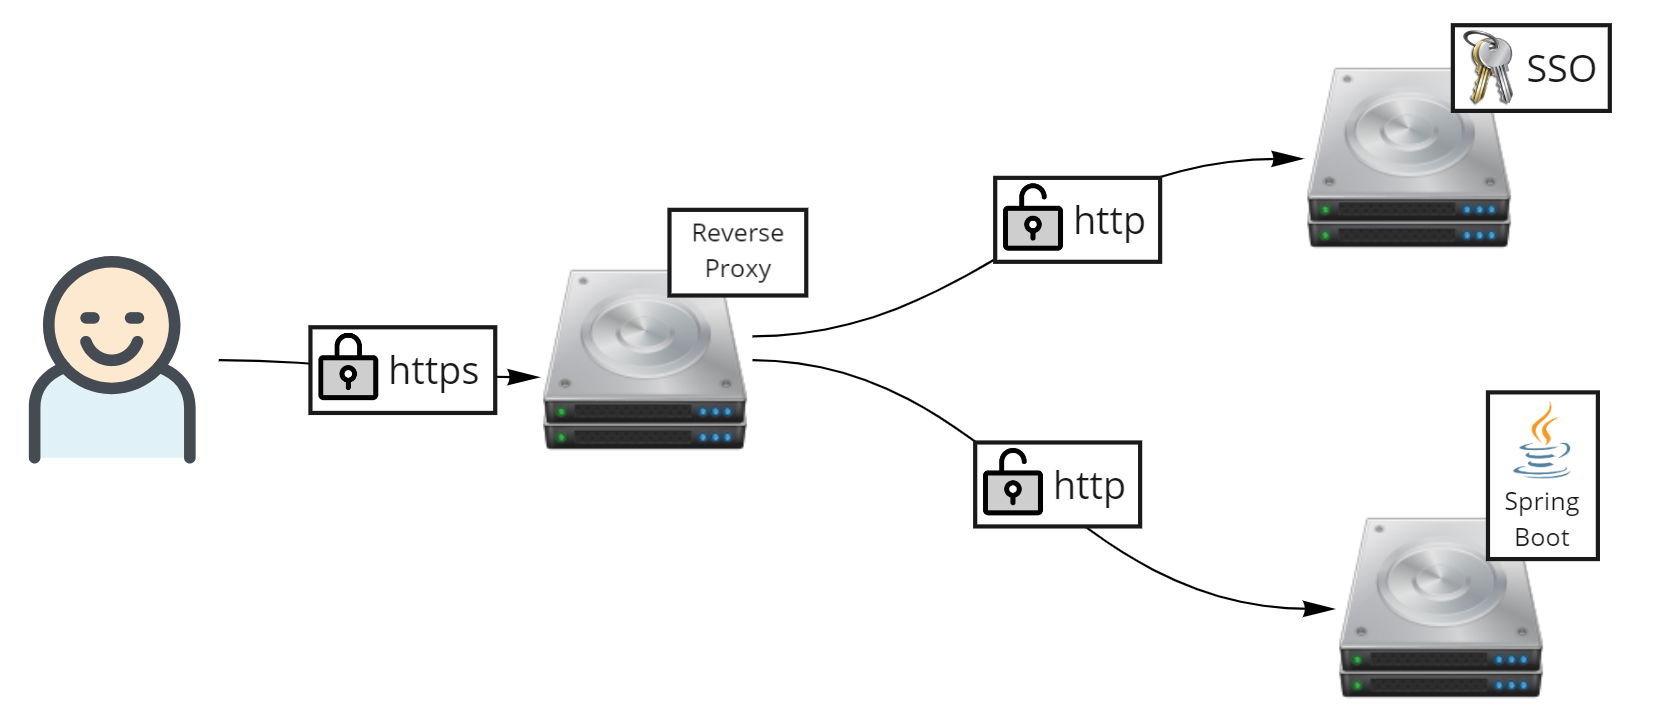
But during implementation, i had this weird condition when Keycloak, behind a reverse proxy for SSL offloader, is redirecting to my Spring Boot application. But Keycloak is not detecting my Spring Boot application as https.
https://keycloak/auth/realms/realm/protocol/openid-connect/auth?
response_type=code&client_id=client-id&redirect_uri=http%3A%2F%2Fspring-boot-app%2Fsso&state=123&
login=true&scope=openid
As we can see, redirect_uri is having http as its protocol, instead of https. Despite my Spring Boot application is being deployed behind a reverse proxy with an SSL offloader.
The workaround is actually quite simple, first thing is that we need to forward request from users into downstream apps, which is Keycloak and Spring Boot. This is primarily being done on reverse proxy or Load Balancer such as F5 or Nginx
X-Forwarded-For: 10.20.81.131
X-Forwarded-Proto: https
X-Forwarded-Host: my.apps.com
But sometimes even after above headers being forwarded, Spring Boot still unaware that it is being accessed as HTTPS. Therefore we need to add one more configuration line in our Spring Boot’s application.properties configuration.
server.forward-headers-strategy=NATIVE
This should be sufficient enough.
Thanks, it was great help after struggling with AI answers and various fixes it suggested.
It was Spring which was at fault here.